Artificial Intelligence (AI) is undeniably reshaping how daily work gets done. When used properly, AI tools can help your team draft proposals, analyze spreadsheets, and summarize complex research in seconds.
In fact, nearly 90% of small businesses, local governments, and schools are actively experimenting with modern AI tools. However, many teams are adopting these helpful tools much faster than they are setting up basic rules and security safeguards.
Understanding the Risks
When employees use random online AI tools without guidance, sensitive information can easily leave your organization. Recent research from IT security firm SentinelOne shows that 70% of organizations have experienced internal data leaks through employee prompts. Further, more than 20% of surveyed organizations reported security breaches stemming from authorized or unauthorized AI use.
To protect your organization, your technology must be more than just convenient. These services need to be productive, secure, and affordable.
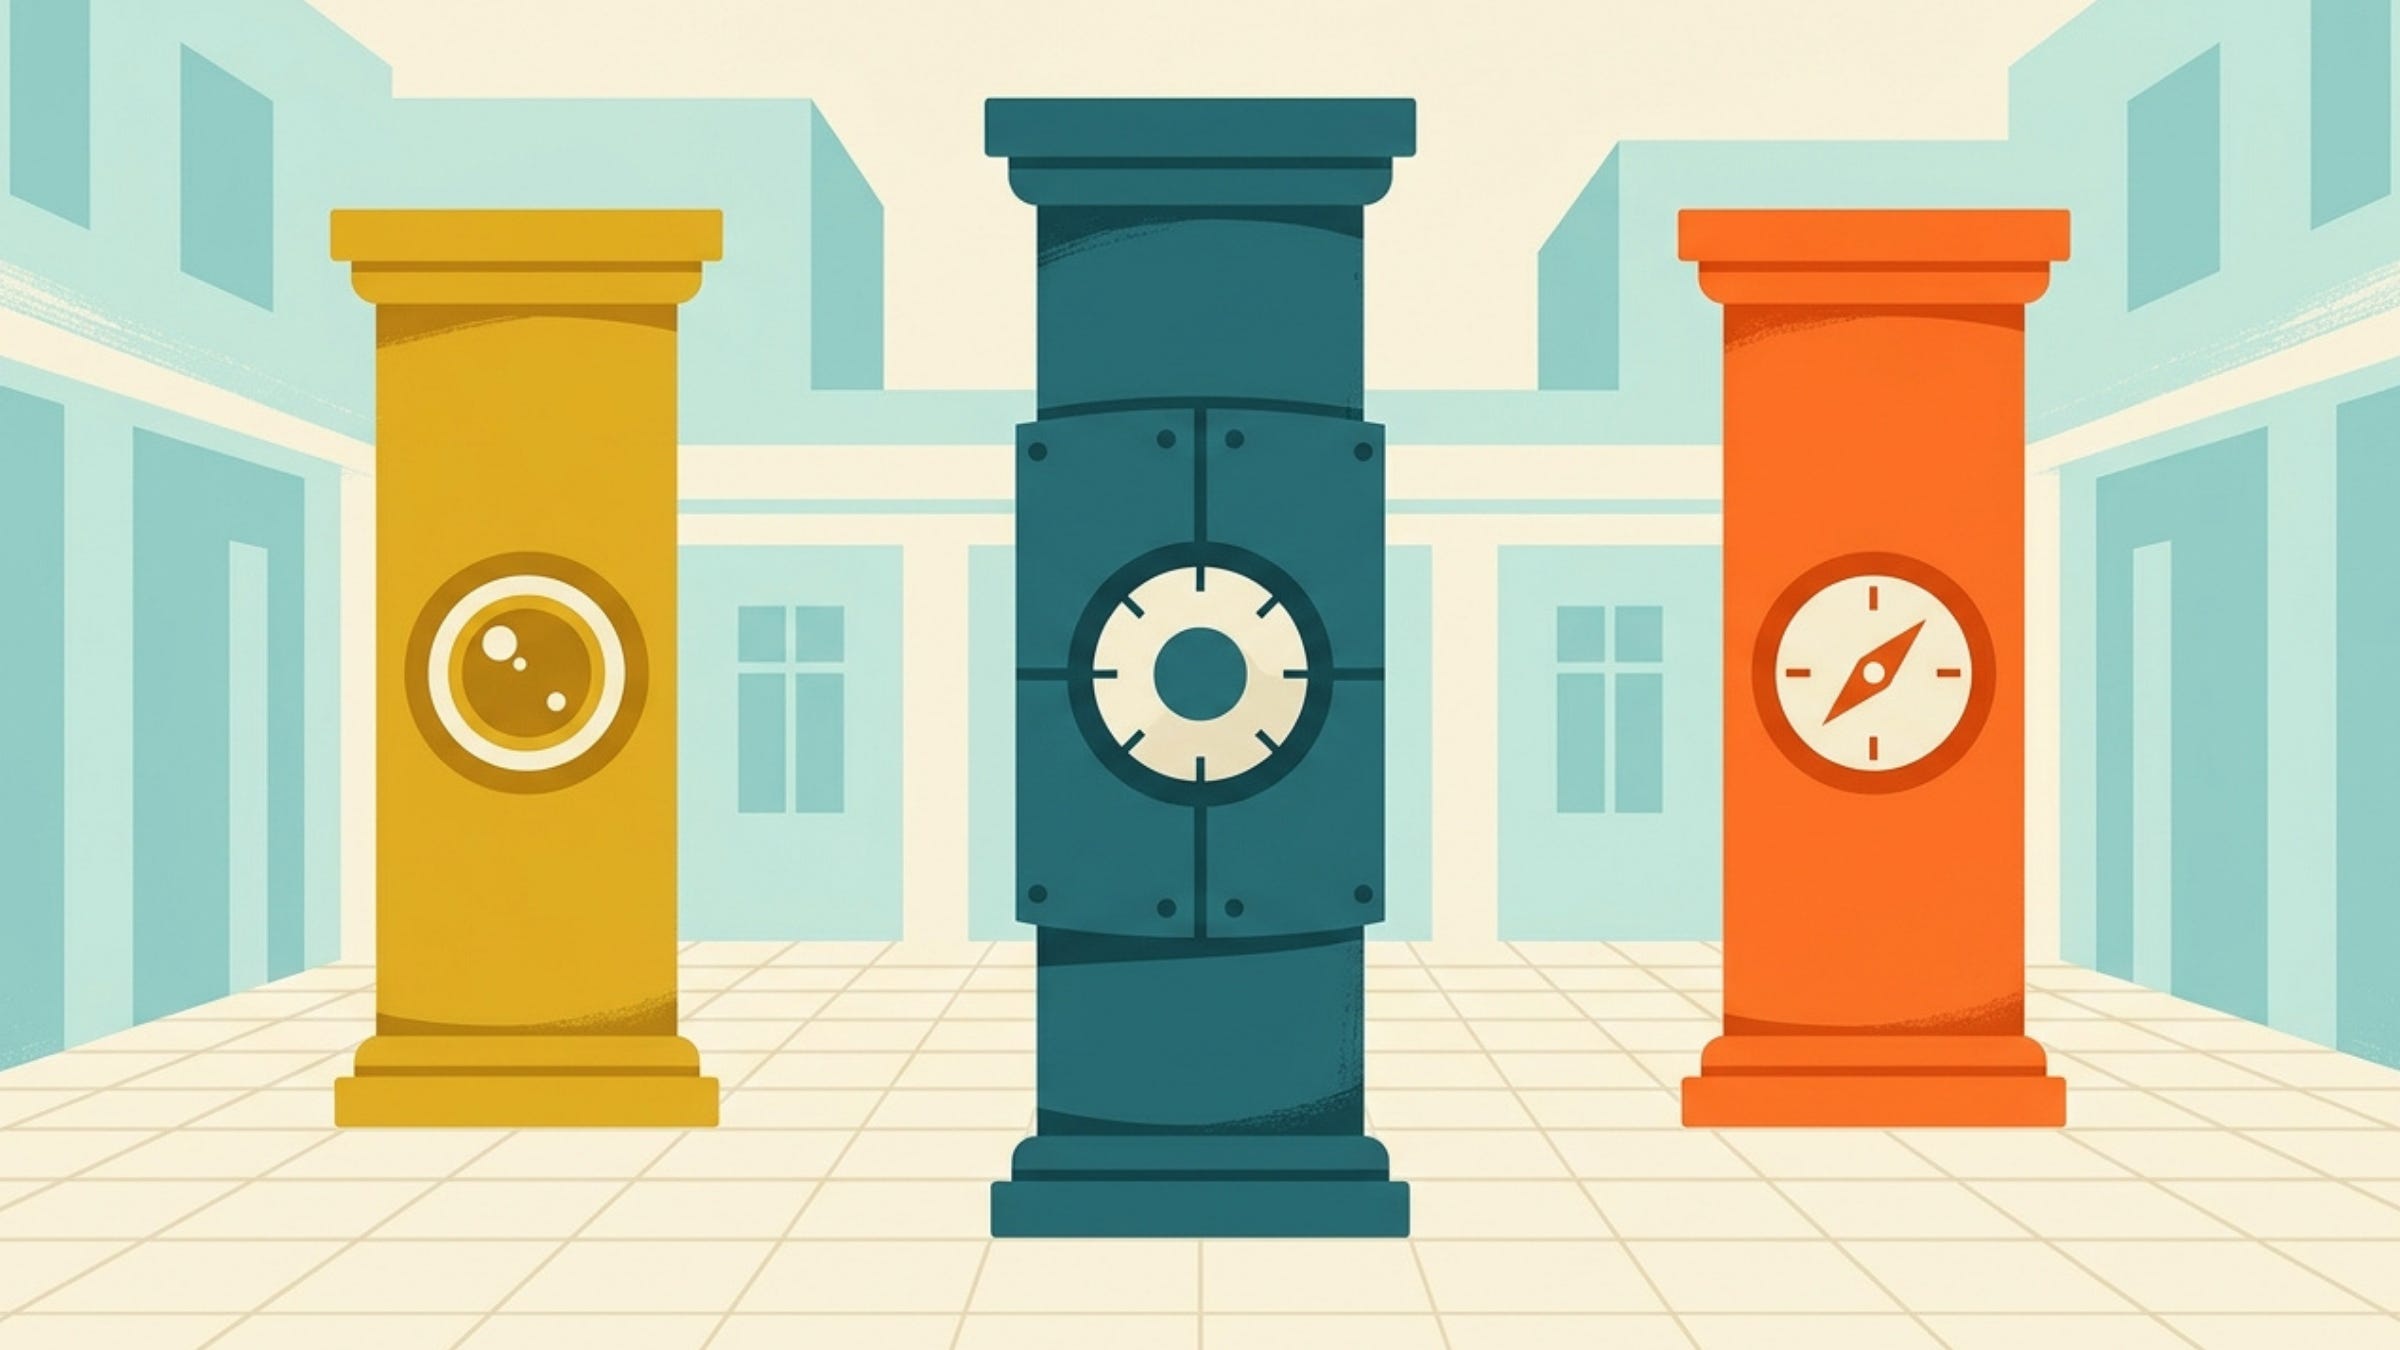
In previous posts, we discussed how focusing on specific use cases and leveraging built-in features in tools you already own will keep costs down while boosting productivity. Protecting that work requires a simple strategy built on three pillars.
The Three Pillars of AI Security
1) See: Bring AI Usage Into Sharp Focus
Most organizations recognize the dangers of Shadow IT (the practice of employees adopting personal or unapproved apps without IT oversight). Shadow AI is the fast-emerging extension of that risk. When team members use personal AI accounts for work tasks, they open your business up to unseen exposure. To manage that risk, you need full visibility into what tools are in play and how your data moves through them.
A strong visibility strategy focuses on a few key practices:
Identifying which AI tools your team employs for daily tasks
Ensuring that everyone logs in using secure business credentials instead of personal accounts
Teaching your team what sensitive business and customer information should never be shared with AI systems
If you do not know what information your team has already shared with AI models, you likely have a hidden risk that needs attention.
2) Secure: Lock Down Access and Safeguard Data
Before you connect AI models to your company files, your underlying permissions must be tight. AI tools can quickly read and organize whatever data they can access, which means a user might accidentally see restricted files through an AI search prompt.
Securing your data requires a proactive approach to access control:
Review user access permissions across all shared folders and cloud drives
Understand exactly what information your AI systems can reach
Monitor third-party integrations as software updates occur over time
3) Steer: Navigate Governance and Chart Your Course
Secure AI lives within clear guardrails. Beyond locking down permissions, you need straightforward policies that guide your team as they use AI.
Setting proper controls involves:
Creating a simple process for employees to request new software tools
Establishing clear boundaries between automated tasks and work that requires human review
Logging system activity so you have clear records if something goes wrong
These guidelines give your team the confidence to use new tools safely while keeping your organization protected.
We Can Help
Through security and readiness assessments, as well as monitoring and management tools, our team can help you understand your current AI security posture, plan your environment, and deploy productive, secure, and affordable solutions.
Contact us or schedule time to connect with a Cloud Advisor to discuss your needs, priorities, and next steps.
About the Author